

The cybersecurity landscape continues to evolve at a breakneck pace, presenting both opportunities and challenges for enterprises globally. With cyber threats becoming increasingly sophisticated, firms must remain vigilant in navigating the complex web of legal compliance and regulatory frameworks.
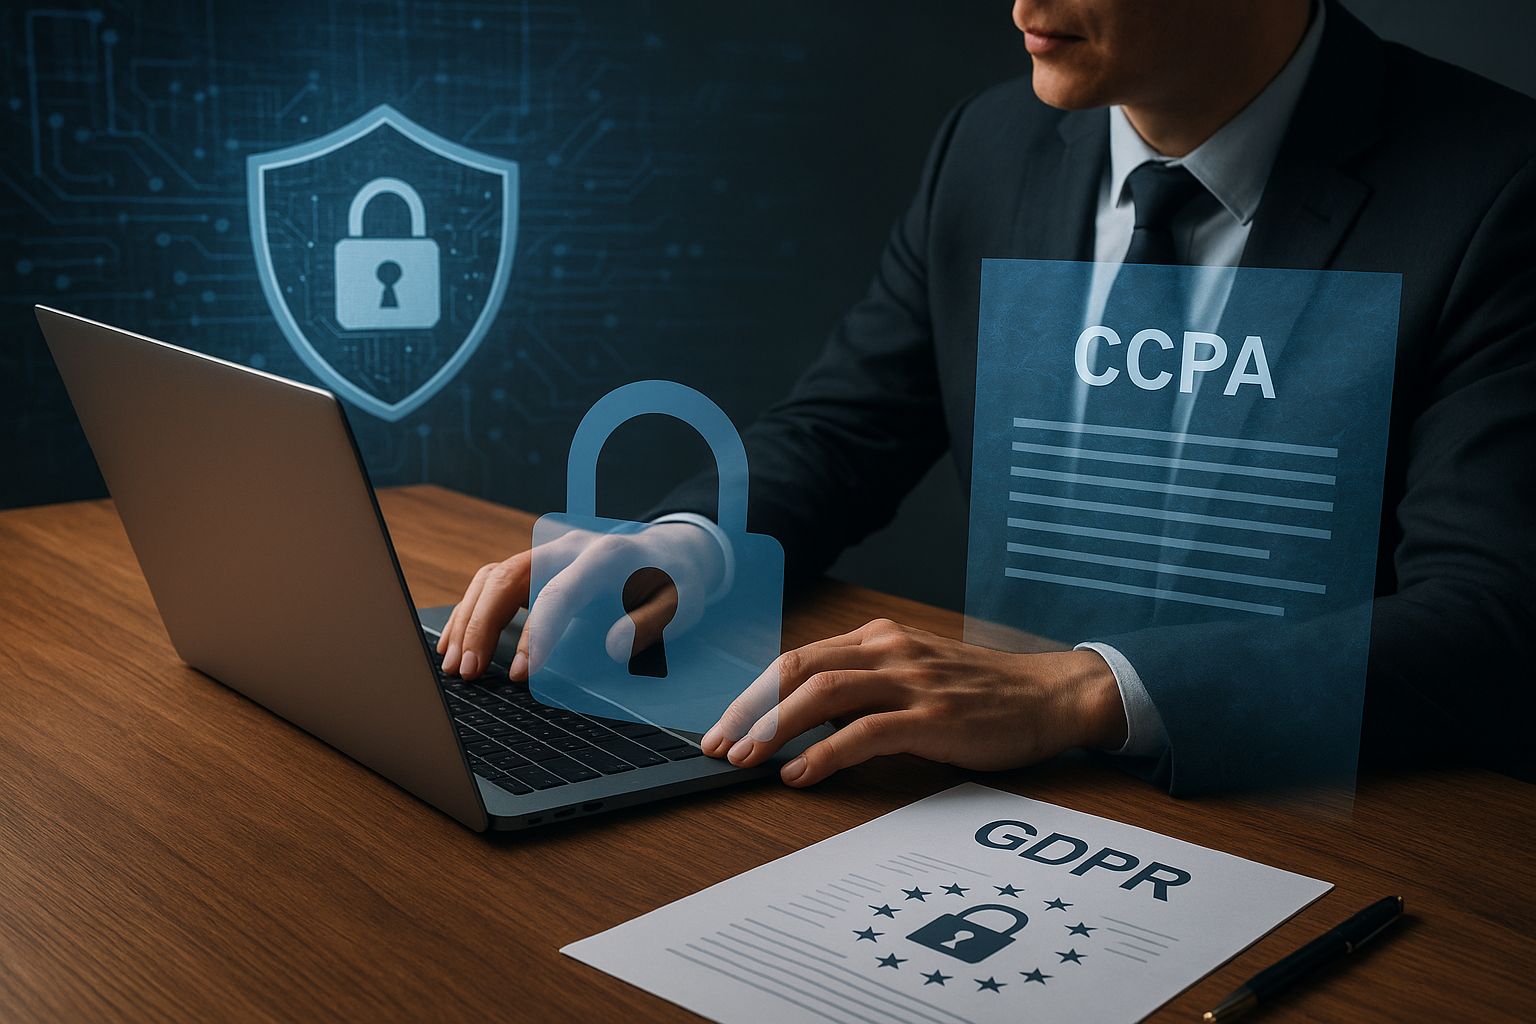
A prevailing trend within this arena is the heightened regulatory scrutiny aimed at safeguarding sensitive data and maintaining robust internal controls. The emergence of regulations such as the General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA) underscores the importance of companies prioritizing data privacy and security.
For instance, a major financial institution recently faced substantial fines due to non-compliance with these regulations. This enforcement action serves as a stark reminder of the potential financial repercussions facing organizations that neglect their cybersecurity obligations.
To develop effective cybersecurity strategies, companies must first conduct comprehensive risk assessments to identify their unique vulnerabilities. Ensuring board-level oversight of cybersecurity initiatives is critical, underscoring the integration between IT security and corporate governance.
Furthermore, establishing a robust incident response plan is integral to mitigating the potential impact of cyber attacks. This plan should encompass clearly defined roles and responsibilities, communication protocols, and a framework for continuous evaluation and improvement.
In addition, advanced analytics and cybersecurity tools can aid in detecting and responding to potential threats in real time, fostering a proactive rather than reactive stance. Businesses must also prioritize employee training initiatives to reinforce a culture of cybersecurity awareness.
As global cyber regulations become increasingly stringent, organizations must continuously adapt to new requirements. A proactive approach involves seeking expert legal counsel to stay abreast of regulatory changes and ensure compliance.
Overall, the intersection of cybersecurity and legal compliance is a critical issue demanding ongoing attention and strategic action from corporate leaders. By fostering an environment of vigilance and innovation, businesses can navigate this complex legal landscape while minimizing risk exposure.