

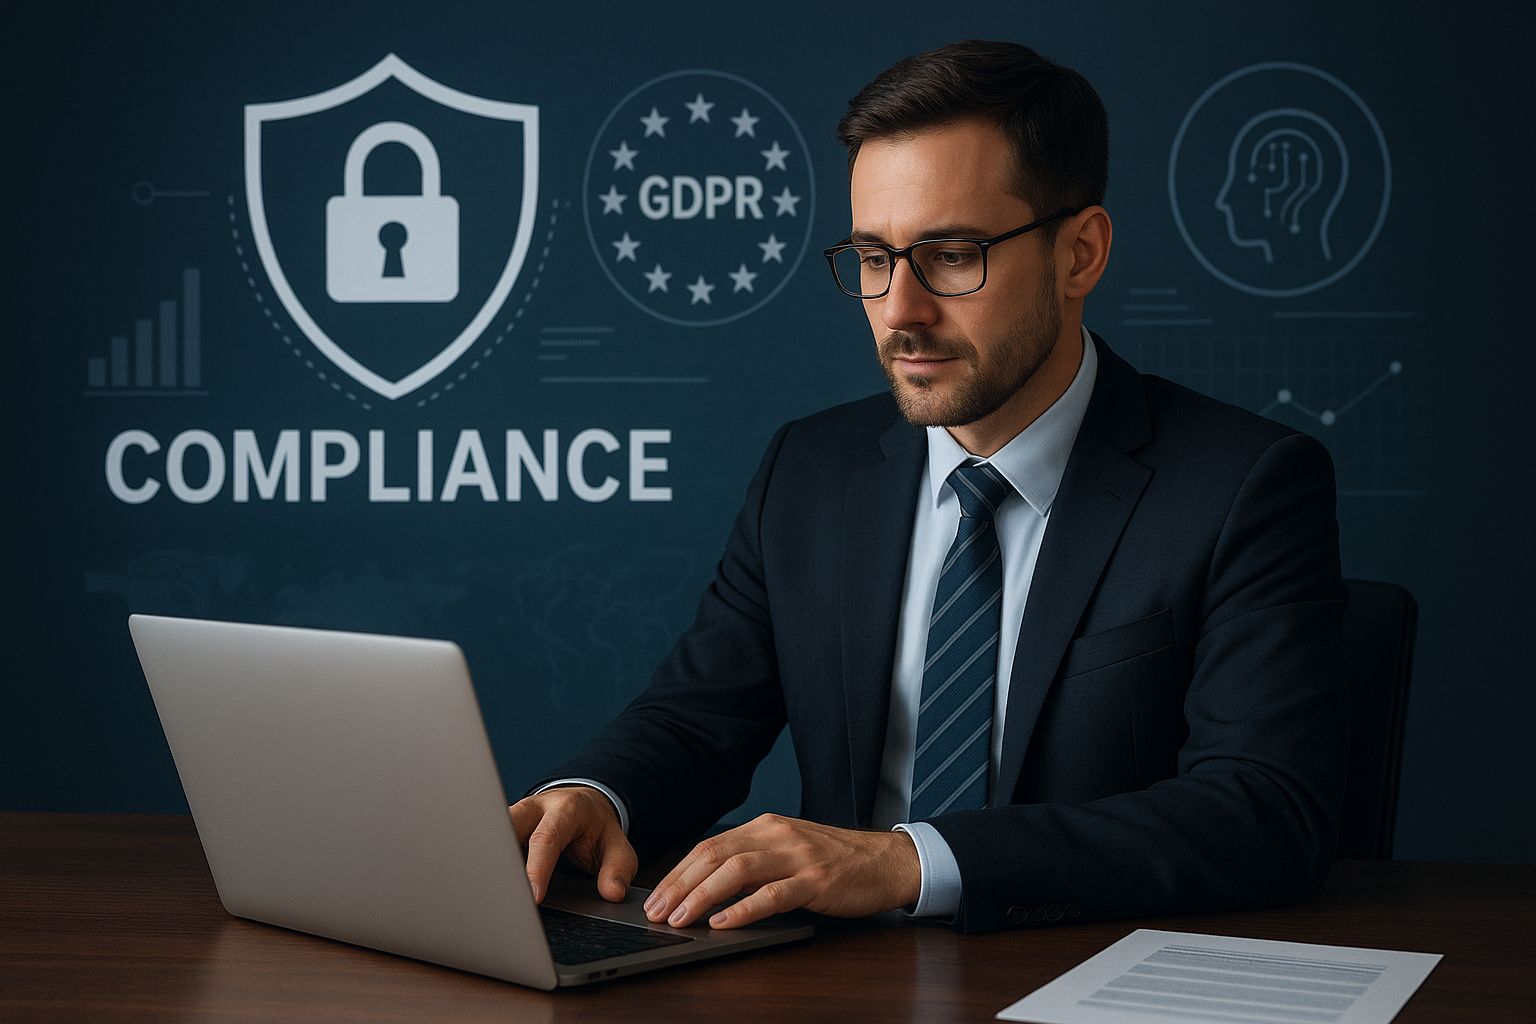
In an era where cyber threats are escalating in frequency and sophistication, regulatory compliance is emerging as a cornerstone of robust cybersecurity strategies for businesses. For many organizations, merely meeting regulatory mandates isn’t enough – the emphasis is increasingly shifting towards leveraging these frameworks to enhance overall cybersecurity posture.
Recent regulatory developments, such as the implementation of the General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA), have spotlighted the need for comprehensive data protection measures. These regulations mandate stringent data management practices that not only protect consumer rights but also fortify organizational defenses against potential breaches.
Businesses are recognizing that aligning with these regulations offers more than just legal compliance; it significantly mitigates risk. By adhering to regulatory standards, companies can proactively manage vulnerabilities and enhance their incident response capabilities. For instance, adopting practices such as regular security audits and risk assessments, stipulated under many regulatory frameworks, can unearth potential security gaps and address them before they are exploited.
Notably, companies across sectors have started integrating compliance requirements into their broader cybersecurity strategies. This integration is not merely for legal adherence but as a strategic approach to bolster cybersecurity. For example, aligning IT and security teams with compliance officers fosters a culture of security awareness, creating more resilient business operations.
One case illustrating this trend is the financial services industry, which has long been a target for cyber-attacks due to the sensitive nature of its data. Banks and financial institutions are incorporating robust compliance programs as part of their cybersecurity strategy, enabling them to not only comply with regulations such as the Financial Services Modernization Act (Gramm-Leach-Bliley Act in the US) but also to secure their information network more holistically.
Moreover, businesses are increasingly taking advantage of technological advancements to maintain compliance and protect themselves. Tools driven by artificial intelligence and machine learning are being employed for automated compliance monitoring and real-time detection of potential threats. These technologies offer scalable solutions that can adapt to the ever-evolving landscape of cyber threats, ensuring that organizations remain one step ahead of potential risks.
In conclusion, leveraging regulatory compliance not just as a checkbox exercise but as a strategic component of cybersecurity practices offers significant advantages. By doing so, businesses not only shield themselves from regulatory penalties but also enhance their resilience against what is an incessant tide of cyber threats. This approach represents a vital paradigm shift from being merely reactive to adopting a proactive, forward-thinking security stance.